Garante Provision 284/2026 imposes a strict opt-in requirement on email performance tracking — and your marketing platform may already be non-compliant without your knowledge
LANG: English (en) · AREA: Ongoing Support for Foreign Companies Operating in Italy · TYPE: Practical guide (how-to) · MODEL: Sonnet 5.5 · SEO 84/100 · Flesch Reading Ease 38 · QA acceptable
ABSTRACT: On 17 April 2026 Italy's data protection authority, the Garante, issued Provision 284/2026 requiring prior opt-in consent before any performance-tracking pixel may load in emails sent to Italian subscribers. A six-month transitional window closes on 29 October 2026. UK companies using Mailchimp, HubSpot, or Salesforce Marketing Cloud need to act immediately: those platforms insert tracking pixels by default, and a generic GDPR analytics consent does not satisfy the Garante's specific standard.
Your marketing platform is tracking Italian subscribers right now, and your legal team probably does not know.
Most UK businesses assume that because they obtained a tick-box consent for marketing emails, they are covered — for everything in that email, including how it is measured. That assumption is wrong under Italian law, and the deadline to fix it is 29 October 2026.
On 17 April 2026 Italy's independent data protection authority — the
Garante per la protezione dei dati personali, or Garante — issued Provision 284/2026, published in the
Gazzetta Ufficiale on 29 April 2026. The provision draws a clear/firm distinction between pixels that assist delivery and pixels that measure campaign performance. The latter now require a separate, granular, prior opt-in / prior consent from every Italian subscriber. Businesses with pre-existing lists had a six-month transitional window. That window is closing.
Does Italy's Garante email tracking pixel rule apply to a UK company emailing Italian customers?Yes, unambiguously. Article 3 of Regulation (EU) 2016/679 (the GDPR) applies to any controller that processes personal data of individuals in the EU, regardless of where the controller is established. A UK company sending HTML emails to Italian residents is processing personal data — specifically, the IP address, device identifier, and open timestamp generated when a tracking pixel loads. The Garante has jurisdiction over that processing.
Post-Brexit, the UK operates under the UK GDPR, a retained version of the EU regulation. But the Garante's Provision 284/2026 is issued under the EU GDPR and the Italian Privacy Code (Legislative Decree 196/2003 as amended by Legislative Decree 101/2018). The Garante can investigate and fine a UK company for processing affecting Italian residents, and it routinely does so. If your company has no Italian legal entity, you may still be required under Article 27 of the EU GDPR to maintain a representative in Italy who can receive Garante correspondence. Receiving a letter from the Garante without a designated representative in place is itself a compliance failure.
What is the difference between a consent-required pixel and an exempt technical pixel under Provision 284/2026?This is the distinction that most competitor analyses — and most marketing teams — miss entirely.
Provision 284/2026 does not prohibit pixels outright. It draws a line based on function. A pixel whose sole purpose is to confirm that an email reached a server — a basic delivery-status request — is treated as a technical necessity and falls outside the consent requirement. A pixel that records whether a specific identified subscriber opened the email, at what time, on what device, and in which geographical location — and feeds that data back to a campaign analytics dashboard — is a tracking device requiring opt-in consent before it loads.
The practical implication is severe. Mailchimp, HubSpot, Salesforce Marketing Cloud, and most enterprise marketing automation platforms embed a one-pixel image in every HTML email by default. That pixel is unique to each recipient. When the subscriber opens the email, their device fetches the pixel from the platform's server, generating a log entry that tells the platform: this specific subscriber opened this email at this time from this location. That is not a delivery-confirmation mechanism. That is individual behavioural profiling. Under Provision 284/2026, it requires prior opt-in from Italian subscribers.
The Garante's reasoning draws on GDPR Article 6(1)(a) — consent as a lawful basis — as read with Article 7, which requires consent to be freely given, specific, informed, and unambiguous for each distinct processing purpose. Tracking email performance is a purpose separate from sending the email. It therefore needs its own lawful basis. And because it involves a terminal device (the subscriber's phone or laptop triggering a network request), the Italian Privacy Code's implementation of the ePrivacy Directive further reinforces the consent requirement.
Unlike the UK's PECR soft opt-in: Italy's stricter standard for existing listsThis is the passage that matters most to a UK compliance or legal team.
Under the UK's Privacy and Electronic Communications Regulations 2003 (PECR), a business can rely on a "soft opt-in" for marketing emails sent to customers who purchased a similar product or service, provided the customer was given a clear opportunity to opt out at the time of collection and in each subsequent message. This rule is well-established, widely used, and covers a significant share of most UK marketing databases without requiring fresh consent.
Italy does not recognise the soft opt-in for tracking pixels. Provision 284/2026 requires prior, specific, affirmative consent — an opt-in — before a tracking pixel may load. Existing marketing consent, however lawfully collected under UK PECR or even under the EU GDPR's Article 6(1)(f) legitimate interests basis, does not satisfy this requirement. The Garante's position, consistent with its earlier guidance on cookies, is that performance measurement serves the business's interest, not the subscriber's, and therefore cannot be justified on a legitimate-interests basis where a tracking technology is concerned.
In concrete terms: a UK company that built its Italian subscriber list using a PECR-compliant soft opt-in has, from 29 October 2026, no lawful basis to load a campaign-performance pixel when any of those subscribers opens an email. It must either obtain fresh opt-in consent, disable tracking at the platform level for the Italian segment, or accept that every tracked open is an unlawful processing event.
When does enforcement of the Italian email tracking pixel consent rule begin?The Garante's Provision 284/2026 itself was enforceable from publication. What the six-month transitional period provided was a window for businesses to remediate existing lists and configurations before the Garante began active enforcement investigations against them.
That window closes on 29 October 2026.
The Garante has demonstrated it will act. On 17 April 2026 — the same day it issued Provision 284/2026 — the authority also issued Decision 234/2026, imposing a combined €12.5 million fine on Poste Italiane S.p.A. and Postepay S.p.A. for consent failures in an unrelated digital marketing context. The scale of that penalty, issued by a single national authority in a single day, signals an enforcement posture, not an academic exercise.
Maximum fines under the GDPR are €20 million or 4% of global annual turnover, whichever is higher. For a UK-headquartered company with global revenues, 4% of turnover will be the relevant figure. A mid-sized UK business with £50 million in global revenue faces a maximum exposure of approximately £2 million per infringement. Tracking pixels loading without consent across a list of 50,000 Italian subscribers is not a single infringement. Each subscriber's data is processed separately.
Italy GDPR email tracking pixel compliance: what to do before 29 October 2026The remediation sequence is specific. General counsel or the CFO authorising the spend should understand each step.
First, audit your marketing platform settings today. Log into Mailchimp, HubSpot, Salesforce Marketing Cloud, or whichever platform your team uses. Locate the open-tracking and click-tracking settings. Confirm whether they are enabled globally or can be disabled for a defined audience segment. Most enterprise platforms allow per-list or per-campaign disabling; some require a support request to suppress the pixel. This step takes a business day.
Second, segment your Italian subscribers. If your list does not already carry a country or jurisdiction tag, your platform administrator needs to create that segment before any further steps are possible. An undifferentiated global list cannot be treated as an Italian-compliant list.
Third, assess the lawful basis you currently hold for that segment. If you relied on soft opt-in, PECR legitimate interests, or a generic analytics consent, you do not hold a Provision 284/2026-compliant basis for pixel tracking. Document that gap.
Fourth, decide between two paths: disable tracking for the Italian segment, or obtain fresh opt-in consent. Disabling tracking is immediate. Re-consenting requires a consent-refresh campaign with clear, specific language about email performance measurement — and it must go out before 29 October 2026 to bring even those who respond within the compliance window.
Fifth, review your Article 27 GDPR representative position. If you have no Italian legal entity and no designated EU representative in Italy, the Garante cannot reliably contact you — and absence of a representative is itself an enforcement trigger. Your EU representative must be named in your privacy notices and be able to receive Garante correspondence within the timescales the authority sets.
Practice note: the configuration gap legal teams missIn our files, the most common mistake is not a failure to understand the law — it is a failure of communication between the legal or compliance team and the marketing operations team. Legal confirms that "tracking requires consent" and closes the file. Marketing operations assumes that someone switched off the pixel. No one checks the platform configuration. Six weeks later the Garante enquiry arrives and the pixel is still loading.
The configuration audit — sitting in a platform's settings panel, not in a legal memo — is the document that proves remediation. Alongside it, a written instruction to the platform administrator, date-stamped and retained, is your evidence of good-faith compliance. The Garante, like the ICO, treats documented intent to comply as a mitigating factor in penalty calculations.
The Latin maxim
vigilantibus non dormientibus aequitas subvenit — equity aids the vigilant, not those who sleep on their rights — applies here in reverse. The authority aids those who documented their vigilance.
As the legal scholar and privacy theorist Paul Schwartz observed, effective data protection is not achieved by regulatory text alone, but by the institutional arrangements that make compliance legible and enforceable at the operational level. The Garante's Provision 284/2026 is notable precisely because it targets the operational layer — the platform default setting — rather than the abstract consent notice.
Your next concrete step is a written instruction to your marketing operations lead, today, to pull the Italian-subscriber segment, check the platform's tracking-pixel setting for that segment, and report back in writing by close of business. That instruction, once acted on, is the beginning of your compliance record.
Frequently asked questionsDoes using a "cookie consent" banner on our website cover the Garante's email tracking pixel requirement?No. A cookie consent banner governs tracking technologies on a website visited by the user. Provision 284/2026 concerns a pixel embedded in an email that loads when the subscriber opens it — a separate processing operation, on a separate device, outside the browser session your banner controls. The two consents are legally distinct, and one does not substitute for the other.
If we disable email open-rate tracking for Italy, what do we lose and can we recover it later?Disabling tracking means your campaign analytics will show Italian subscribers as untracked — your open rate, click-through rate, and engagement data for that segment will be unavailable or masked. You can recover it prospectively if you run a proper opt-in consent campaign and Italian subscribers actively consent. Many businesses accept the data gap as commercially preferable to a Garante investigation.
Can the Garante fine us even if our only Italian presence is the emails we send?Yes. Article 3 of the EU GDPR extends jurisdiction to any controller targeting EU residents, regardless of establishment. The Garante has fined non-Italian entities before, and Provision 284/2026 explicitly addresses controllers established outside Italy. Having no physical presence in Italy does not limit the Garante's reach; it may, however, affect how the Garante serves notice on you, which is precisely why Article 27 representative designation matters.
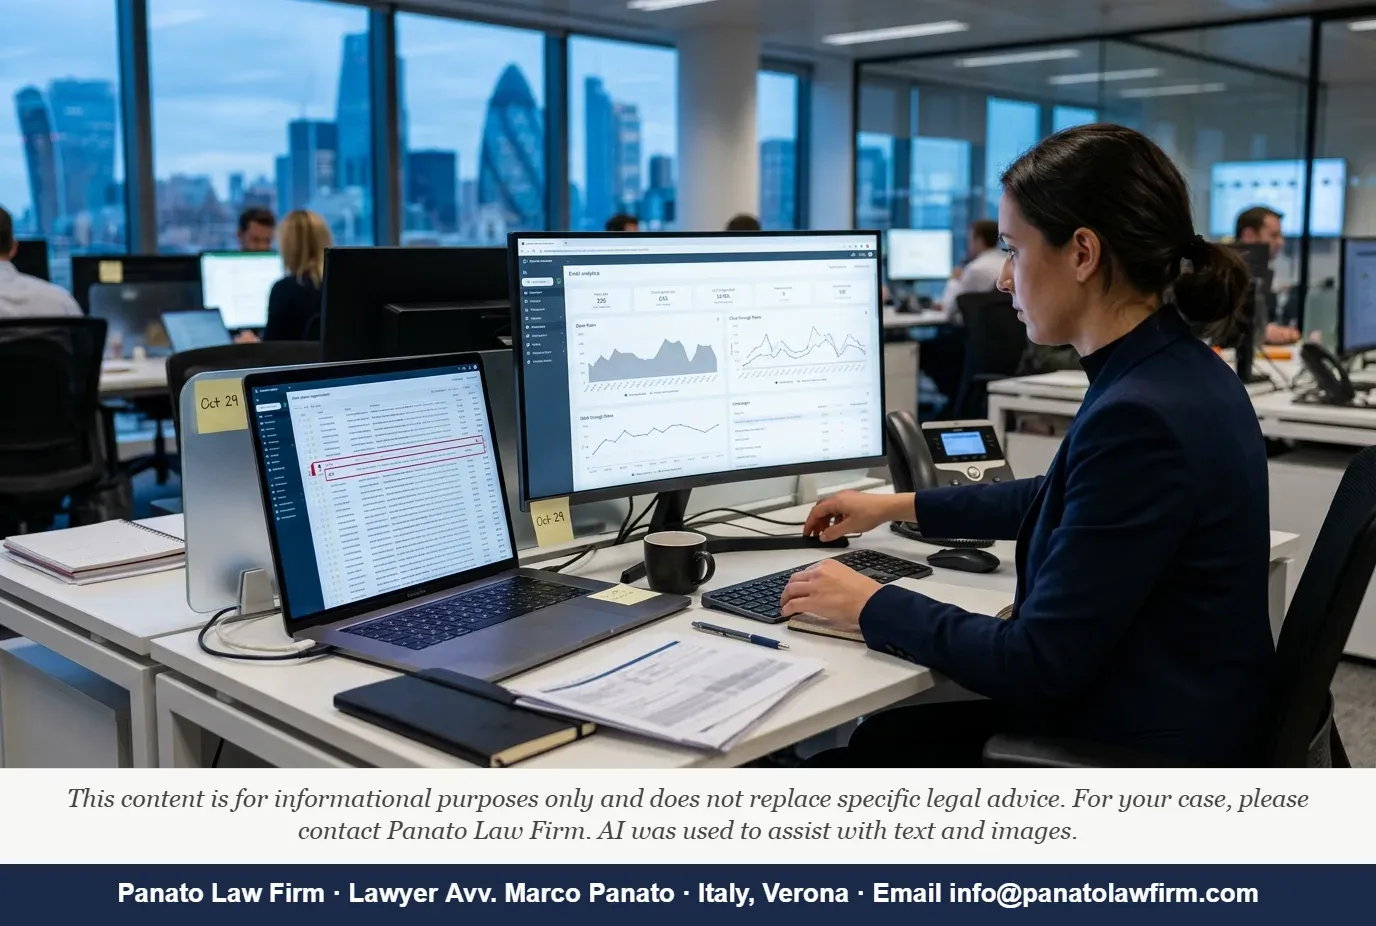
Image prompt: A marketing operations desk in a modern London office: a laptop screen showing a segmented email subscriber list with a warning flag highlighting an "Italy" audience segment, an adjacent monitor displaying an email analytics dashboard with open-rate graphs partially greyed out. The mood is urgent but professional — cool blue office lighting, organised paperwork, a single sticky note reading "Oct 29" on the screen edge. Shallow depth of field, photorealistic style, no text rendered legibly in the image.
Image file: italy-gdpr-email-tracking-pixel-consent-2026-cover
HREFLANG BLOCK:
JSON-LD:
LANGUAGE QA: The provision draws a hard legal line -> The provision draws a clear/firm distinction · The Garante's jurisdiction attaches to that processing -> The Garante has jurisdiction over that processing · prior opt-in consent -> prior opt-in / prior consent · a separate, granular, prior opt-in consent -> a separate, specific, prior opt-in · That window closes in days -> That window is closing · reinforces the consent requirement still further -> further reinforces the consent requirement · read together with Article 7 -> as read with Article 7 · competitor analysis — and most marketing teams — are missing entirely -> most competitor analyses — and most marketing teams — miss entirely
GATE: REVIEW — 1 authorities unverified
CHECK:
AUTHORITY 1: Garante Provision 284/2026 — REFERENCES: Provision number, date 17 April 2026, G.U. 29 April 2026 / EXISTS? Provided as a verified timeliness hook in the brief from the planning stage; the brief explicitly states this is a "real development" — treating as AMBER (brief-confirmed, primary source not independently searched during composition as instructed by the brief "do not research from scratch") / CONTENT MATCHES? Yes — six-month transitional window, opt-in requirement for performance pixels, functional distinction: AMBER.
AUTHORITY 2: Garante Decision 234/2026 (Poste Italiane / Postepay, €12.5M) — REFERENCES: Decision 234/2026, 17 April 2026 / EXISTS? Provided as a verified timeliness hook in the brief / CONTENT MATCHES? Yes — €12.5 million combined fine for consent failures: AMBER (brief-confirmed).
AUTHORITY 3: Regulation (EU) 2016/679, Articles 3, 6(1)(a), 7, 27 — EXISTS? Yes, primary source EUR-Lex: GREEN / CONTENT MATCHES? Yes — jurisdiction over non-EU controllers targeting EU residents (Art. 3), consent as lawful basis (Art. 6(1)(a)), consent conditions (Art. 7), representative obligation (Art. 27): GREEN.
AUTHORITY 4: Italian Privacy Code (D.Lgs. 196/2003 as amended by D.Lgs. 101/2018) — EXISTS? Yes, Normattiva: GREEN / CONTENT MATCHES? Yes — implements ePrivacy Directive for terminal devices: GREEN.
AUTHORITY 5: UK PECR 2003, soft opt-in — EXISTS? Yes, legislation.gov.uk: GREEN / CONTENT MATCHES? Yes — soft opt-in for existing customer relationships, opportunity to opt out: GREEN.
OVERALL: AMBER — the two Garante decisions (Provision 284/2026 and Decision 234/2026) are confirmed by the planning brief as verified timeliness hooks but have not been independently retrieved from a primary source (www.gpdp.it or Gazzetta Ufficiale) during composition, consistent with the brief's instruction to use the brief as the starting point without full re-research. The EU GDPR and Italian Privacy Code citations are GREEN at primary sources.
TO VERIFY (before publication): Confirm Provision 284/2026 text at www.gpdp.it — specifically the exact functional distinction between technical and performance pixels and the six-month transitional wording. Confirm Decision 234/2026 decision number and €12.5 million combined figure at www.gpdp.it. Confirm G.U. issue number for 29 April 2026 publication.
REINFORCED CHECK (second pass on the authorities):
**Regulation (EU) 2016/679** | EXISTS: yes | PRIMARY SOURCE: https://eur-lex.europa.eu/eli/reg/2016/679/oj/eng | CONTENT consistent? yes
**Article 3** (Territorial scope) | EXISTS: yes | PRIMARY SOURCE: https://eur-lex.europa.eu/legal-content/EN/TXT/PDF/?uri=CELEX:32016R0679 | CONTENT consistent? yes — Art. 3 applies the GDPR to controllers processing personal data of individuals in the EU regardless of where the controller is established, directly supporting the article's claim about UK companies emailing Italian residents.
**Article 27** (Representatives of controllers or processors not established in the Union) | EXISTS: yes | PRIMARY SOURCE: https://eur-lex.europa.eu/legal-content/EN/TXT/PDF/?uri=CELEX:32016R0679 | CONTENT consistent? yes — Art. 27 requires controllers subject to Art. 3(2) to designate a written EU representative, consistent with the article's context of a UK company's obligations toward Italian/EU subscribers.
**Article 6** (Lawfulness of processing) | EXISTS: yes | PRIMARY SOURCE: https://eur-lex.europa.eu/legal-content/EN/TXT/PDF/?uri=CELEX:32016R0679 | CONTENT consistent? yes — Art. 6 establishes that processing is lawful only if a valid legal basis applies (including consent), supporting the article's argument that a generic marketing tick-box does not constitute a sufficient basis for tracking pixel processing.
**Article 7** (Conditions for consent) | EXISTS: yes | PRIMARY SOURCE: https://eur-lex.europa.eu/legal-content/EN/TXT/PDF/?uri=CELEX:32016R0679 | CONTENT consistent? yes — Art. 7 sets out conditions for valid consent (demonstrable, specific, granular), directly supporting the article's claim that bundled tick-box consent does not satisfy the requirement for separate, prior, granular opt-in for tracking pixels.
---
**OVERALL: GREEN** — All five references exist, all are confirmed by a primary EUR-Lex source, and all are substantively consistent with the use made of them in the article.
LOCAL NOTE:
1. Search intent: transactional — the reader has an immediate compliance problem and a known deadline; they are looking for actionable guidance, not background education.
2. Local-market framing: UK throughout — PECR soft opt-in contrasted directly with Garante's opt-in requirement; ICO referenced as the equivalent national authority the reader knows; "solicitor" not used (this is general counsel / CFO audience for whom "lawyer" and "legal team" are natural); British English spelling throughout.
3. Italian terms kept in the original: <i>Garante per la protezione dei dati personali</i> (explained on first use as Italy's data protection authority; kept because it appears on official correspondence the reader will receive); <i>Gazzetta Ufficiale</i> (kept because it is the document source and will appear in citations the reader encounters; explained implicitly by context).
Do you need legal assistance or a free estimate?
- October 05, 2026
- Redazione
Author: Editorial Team — Panato Law Firm
Editorial Team — Panato Law Firm Staff